
SQL injection scanner: Detect and validate SQL injection vulnerabilities with Invicti
SQL injection (SQLi) remains one of the most dangerous and widely exploited web application vulnerabilities. It allows attackers to interfere with server-side database queries, access sensitive data, and in some cases take control of application functionality.
An SQL injection scanner helps you identify these security flaws through automated vulnerability scanning by testing how your web app handles untrusted input. The Invicti web vulnerability scanner uses dynamic application security testing to analyze running applications from the outside, finding SQL injection and other flaws that are actually reachable and exploitable across modern architectures, including APIs and distributed endpoints.
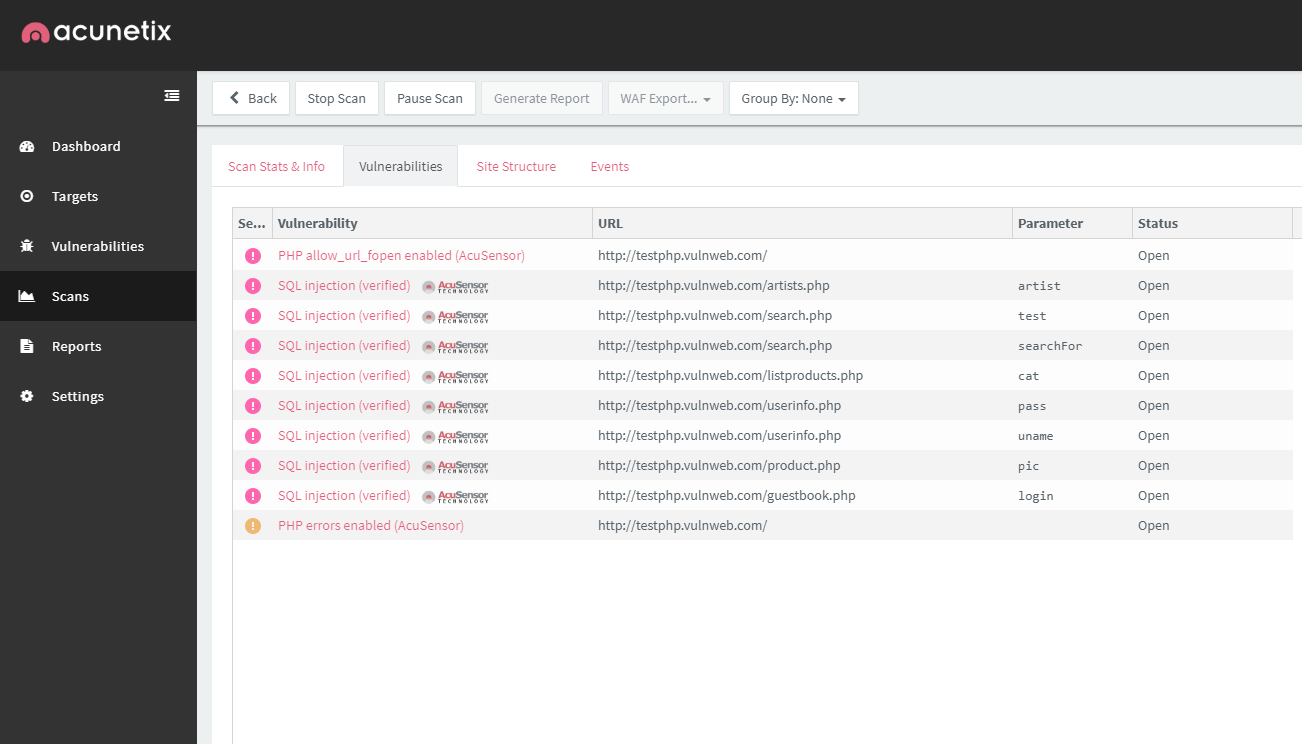
How SQL injection scanning works
Automated SQL injection scanning is more than sending payloads and looking for errors. A modern scanner follows a structured process to identify and confirm real vulnerabilities:
- Crawl the application – Invicti maps your web app, discovering pages, API endpoints, parameters, and input vectors exposed through forms, headers, and HTTP requests.
- Identify injection points – It detects where user input is processed in server-side logic and could be used in SQL queries.
- Inject test payloads – The scanner sends carefully crafted SQL payloads, including boolean-based, error-based, and time-based variations, to trigger different SQLi behaviors.
- Analyze responses – It evaluates how the application responds, looking for behavioral changes rather than simple string matches.
- Validate findings – Where possible, Invicti confirms exploitability by demonstrating how the injection affects the application or database, reducing false positives.
- Report results – Verified vulnerabilities are reported with technical details, including request/response data and remediation guidance.
This approach allows Invicti to perform testing that corresponds to a full range of SQL injection attack techniques, including:
- In-band SQL injection – where data is retrieved through the same channel as the attack
- Blind SQL injection – including Boolean-based and time-based techniques that rely on indirect signals
- Out-of-band SQL injection – where external channels are used to confirm exploitation
By focusing on behavior and validation rather than simple pattern matching, Invicti delivers more accurate results with fewer false positives.

Automated scanning vs. manual testing tools
Security professionals often rely on penetration testing tools such as sqlmap or Burp Suite for manual SQLi exploitation. These tools are powerful for deep pentesting, but they require time, expertise, and predefined targets.
Invicti supports a different – and complementary – approach:
- Scales across applications – Automatically scans entire web apps and APIs to find potential injection points across all exposed endpoints
- Supports continuous testing – Runs automated scans during development and integrates into CI/CD workflows
- Prioritizes real risk – Highlights security vulnerabilities that are reachable and validated, helping teams focus on what matters
- Reduces manual effort – Minimizes the need for repetitive pentesting tasks by identifying issues early
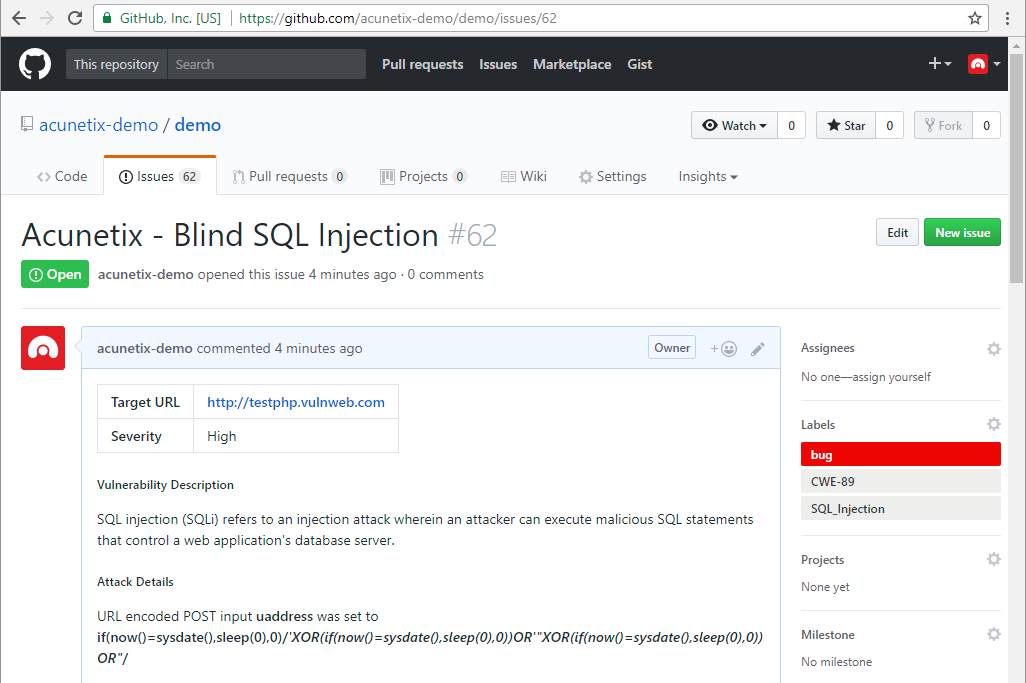
- Integrates into development workflows – Connects with issue trackers and DevOps pipelines to streamline remediation
In practice, automated vulnerability scanning and manual penetration testing work best together. Invicti helps you discover and validate SQLi vulnerabilities at scale, while tools like sqlmap can be used for deeper exploitation and analysis when needed.
Beyond SQL injection detection
SQL injection is only one part of the attack surface. Invicti provides broader web application security and API security testing to help identify and manage vulnerabilities across your environment.
Key capabilities include:
- Comprehensive vulnerability coverage – Detects common web vulnerabilities such as cross-site scripting (XSS), CSRF, and security misconfigurations
- API and endpoint security testing – Scans modern API-driven architectures alongside traditional web app functionality
- Accurate results with validation – Uses advanced techniques to reduce false positives and deliver actionable findings
- Authentication support – Tests authenticated areas of applications to uncover vulnerabilities behind login barriers
- Developer-focused reporting – Provides detailed technical insights, including HTTP request and response data, to support faster fixes
- Workflow integration – Connects with tools like Jira, GitHub, GitLab, and Jenkins to support remediation workflows
- Flexible deployment – Available on-premises and as an online service
By combining detection, validation, and integration, Invicti helps teams move efficiently from vulnerability discovery to remediation.
Frequently asked questions
An SQL injection scanner is a security tool used in vulnerability scanning and penetration testing to automatically test web applications for SQLi vulnerabilities. It identifies input points, sends test payloads, and analyzes responses to detect potential injection flaws.
Automated scanners crawl your web app, identify input fields and API endpoints, inject SQL payloads through HTTP requests, and analyze server-side responses. Advanced tools also validate findings to confirm whether a vulnerability is exploitable.
- In-band SQL injection returns results directly in the application response
- Blind SQL injection (including boolean-based and time-based techniques) relies on indirect signals
- Out-of-band SQL injection uses external systems to confirm exploitation
sqlmap is a manual tool used in penetration testing to exploit known SQL injection points. Invicti is an automated vulnerability scanning solution that discovers and validates SQLi vulnerabilities across entire web applications and APIs. It is designed for continuous testing and integration into development workflows.
Professional scanners like Invicti are designed to perform automated testing in a controlled and non-destructive way. They use safe payloads and validation techniques to detect vulnerabilities without disrupting application functionality or damaging data.
Recommended Reading
Learn more about prominent vulnerabilities, keep up with recent product updates, and catch the latest news from Invicti.
“We use Invicti as part of our Security in the SDLC and to test code in DEV and SIT before being promoted to Production.”
Kurt Zanzi, Xerox CA-MMIS Information Securtiy Office, Xerox