
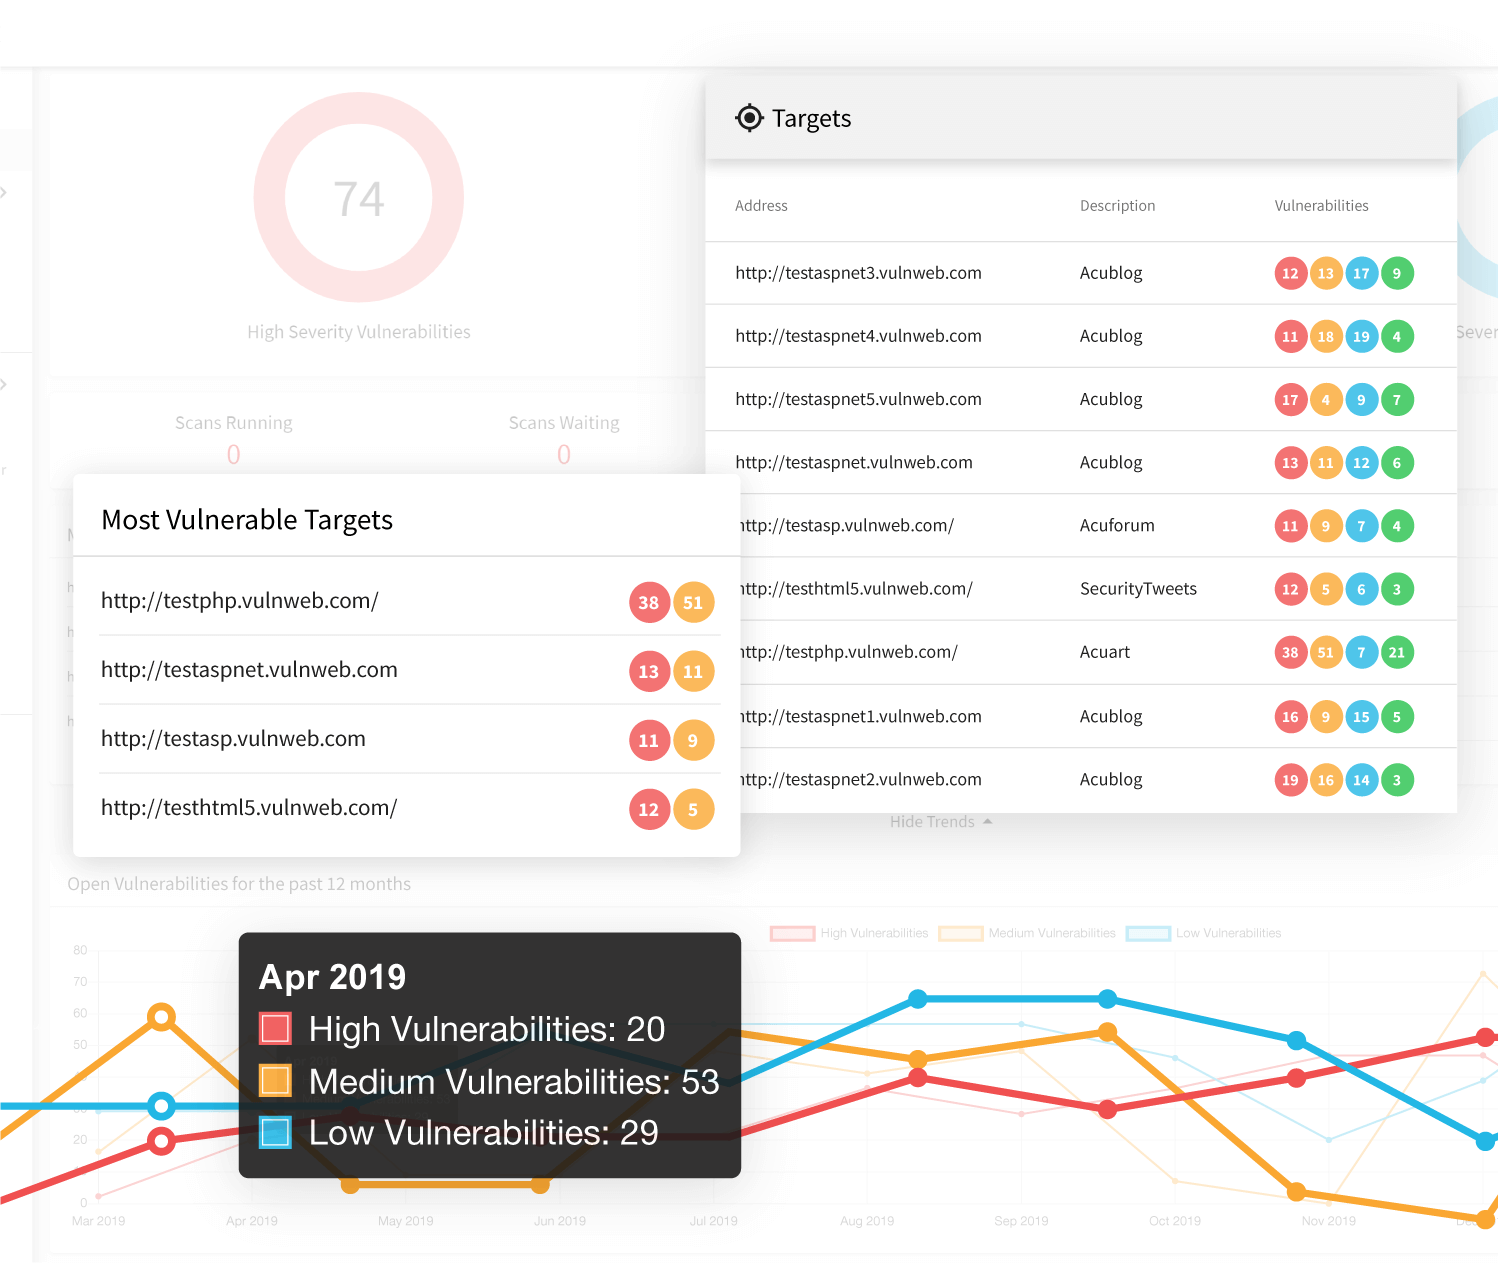
Ultimate Flexibility and Scalability
Invicti is the most flexible web application security scanner on the market. Though both Invicti and Qualys offer a software-as-a-service model, Invicti also offers an on-premise version of its web vulnerability scanner, perfect for security teams that prefer to run tools within their own infrastructure, or for an internal penetration testing setup. Invicti can run on Windows, Linux, and macOS, meaning Invicti will work no matter what stack you depend on. For companies that prefer to perform their web application vulnerability scanning from their own infrastructure but need to scale it up with time, Invicti offers the multi-engine setup. With Invicti multi-engine, security analysts can control multiple remote scanners, access results, and perform vulnerability management from a single web-based console.Comprehensive, Fast Scanning
As part of a complete information security program, you need to perform frequent web application security testing. This includes scanning the entire web application attack surface with a tool designed to identify security vulnerabilities in the OWASP Top Ten and beyond, including SQL Injection, Cross-site Scripting (XSS), and local file inclusion (LFI). Invicti was built from the ground up for web application scanning. It can identify the full range of web application vulnerabilities on any kind of web application, from open-source content management systems like WordPress to commercial off-the-shelf frameworks to code developed specifically for your business. And it does so with a minimal rate of false positives, allowing your security team to move as quickly as possible from scan results to remediation. With Invicti, you do not have to sacrifice accuracy for speed. The scanning engine for the Invicti web vulnerability scanner is optimized for speed. The cutting-edge engine provides increased scan speed for all target applications.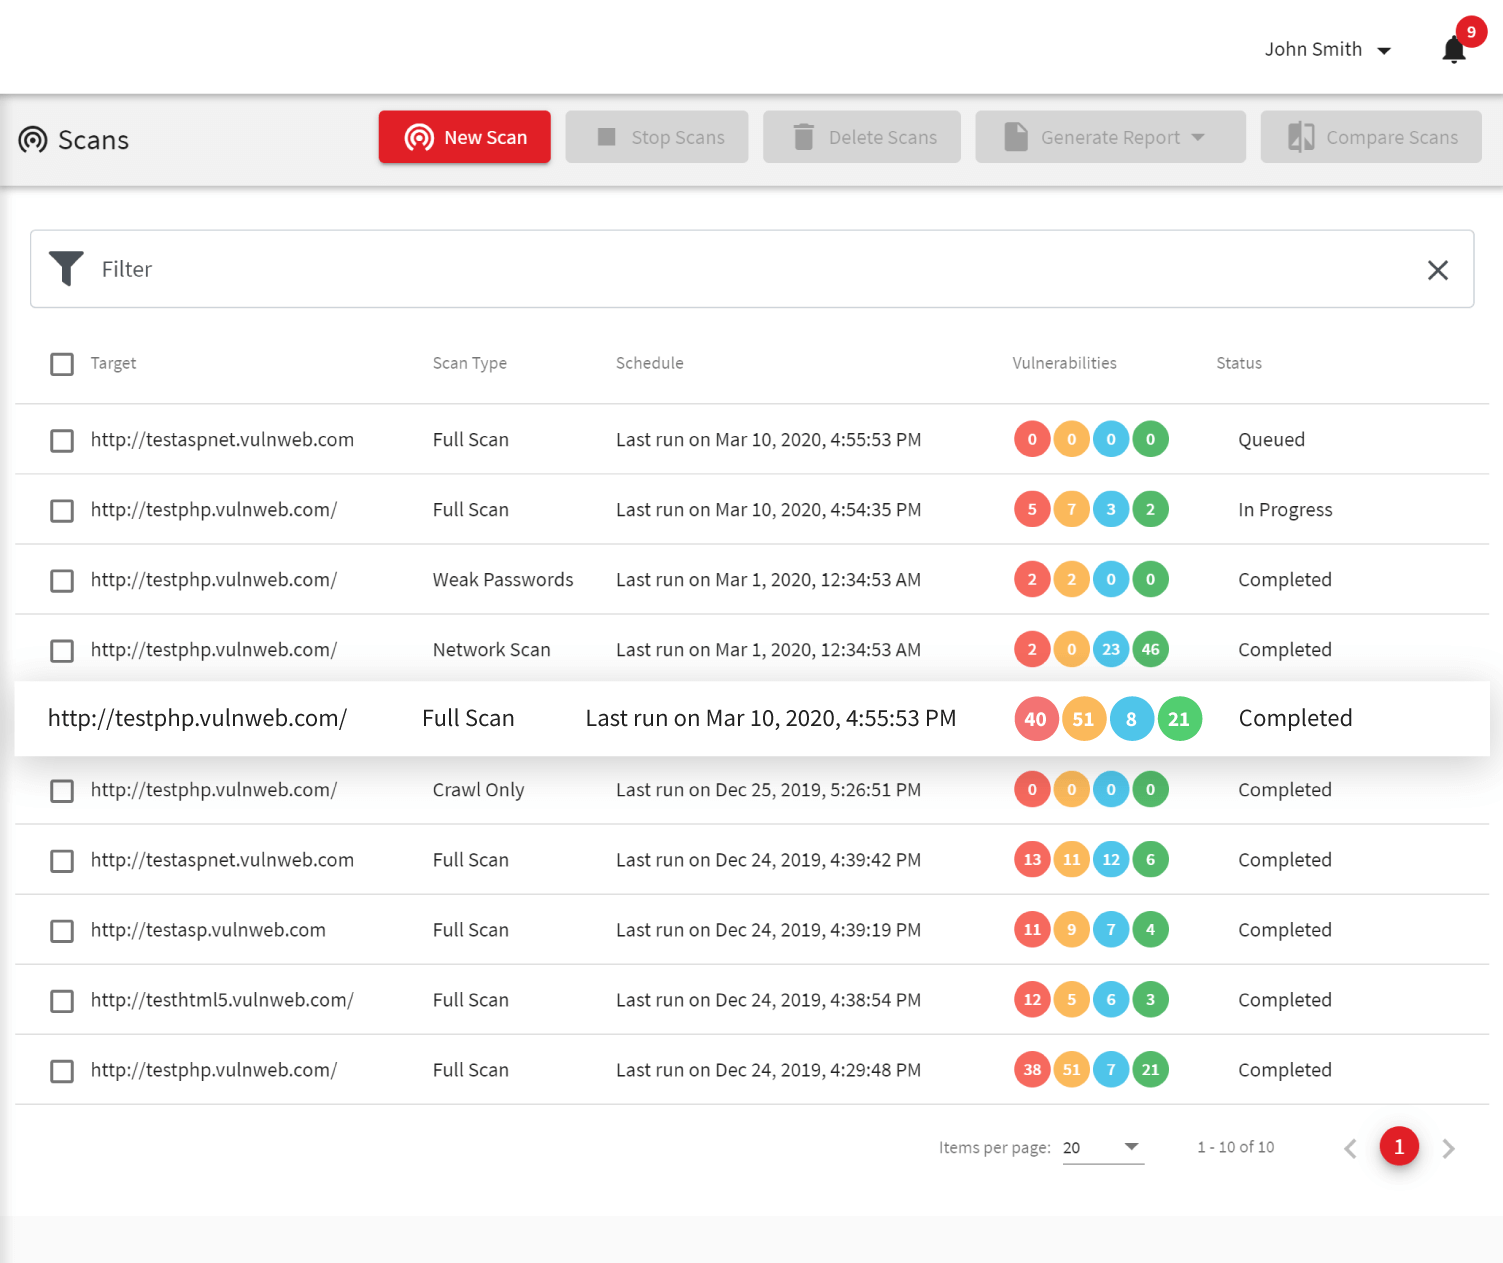
DeepScan Technology
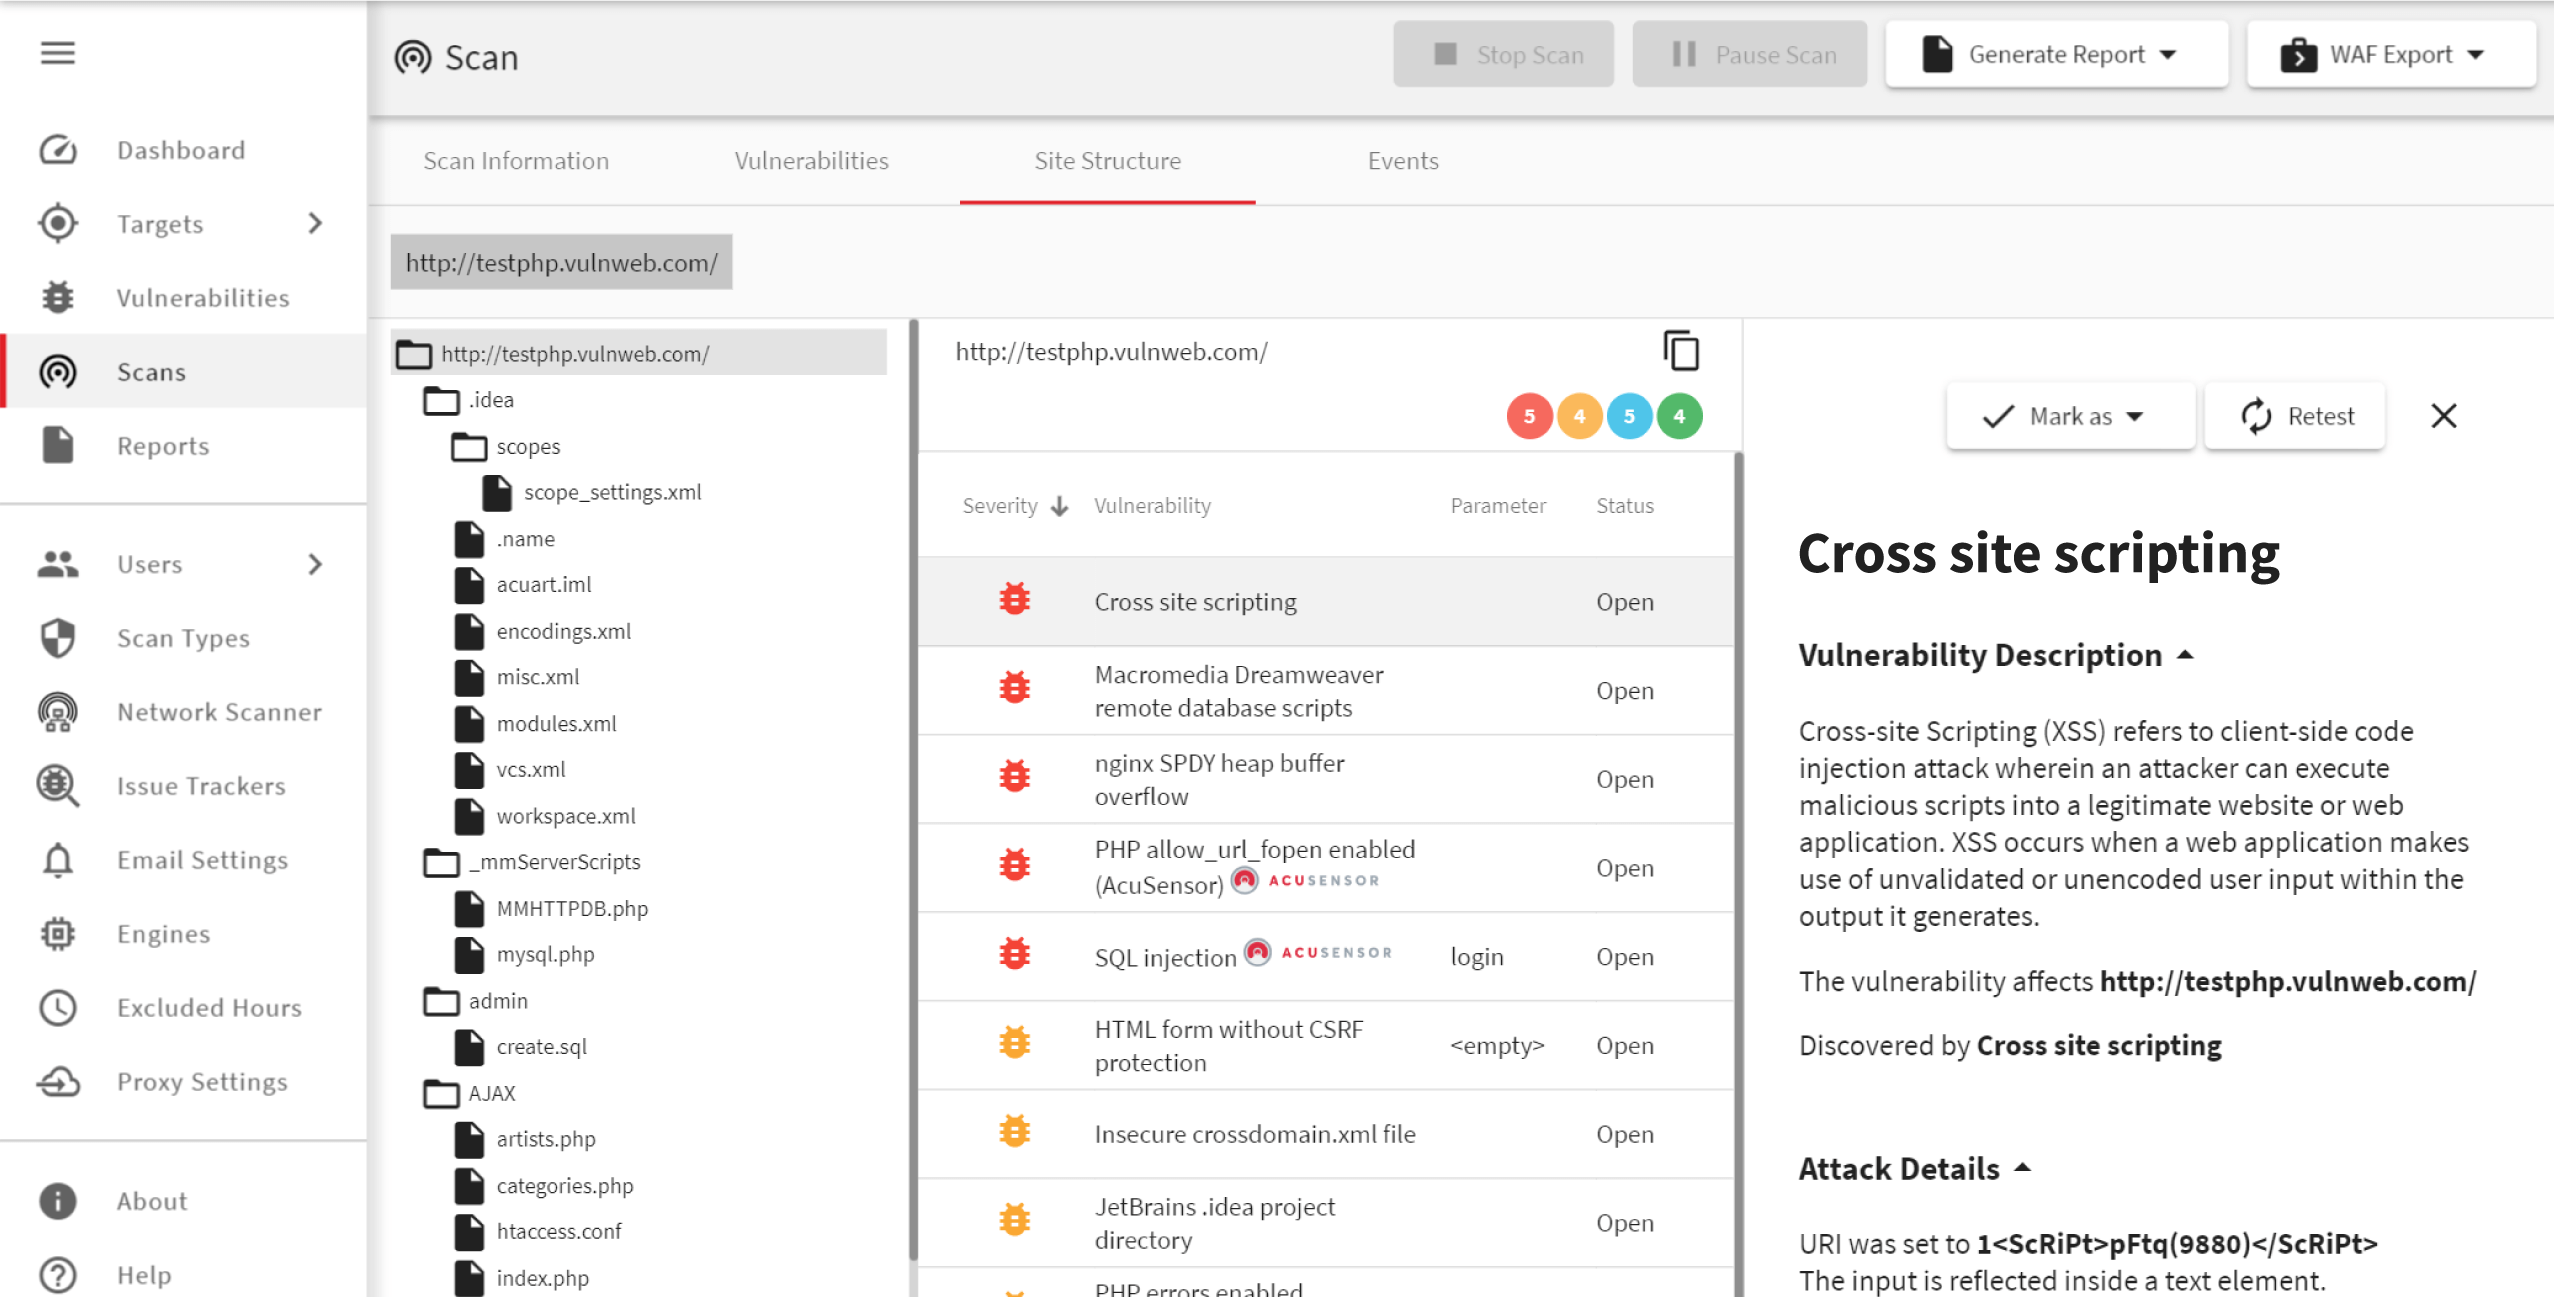
As web application technology moves toward single-page applications that depend on JavaScript and HTML5, you need a scanner that can map out all of the functionality of single-page applications, identify every input field, and detect the full spectrum of vulnerabilities with confidence. Invicti gives you this with the power of the DeepScan engine. In 2013, Invicti was the first web application security scanner to develop a scanning technology focused on applications that run so much logic on the client side. Security researchers at Invicti developed a technology and implemented it in our web application security scanner as DeepScan.The Power of Gray-Box Testing
Invicti not only offers best-in-class black-box testing, but also lets you go beyond conventional black-box testing with the power of AcuSensor. Though Qualys and its competitors can perform dynamic application security testing (DAST), otherwise known as black-box testing, they lack the features to go deeper. AcuSensor, available exclusively with the Invicti vulnerability scanner, is an agent that runs on the web server and gives the scanner deeper information about PHP, ASP.NET, and Java web applications. It allows you to perform interactive application security testing (IAST), or gray-box testing. AcuSensor gives the scanner source code visibility for PHP applications and stack trace visibility for ASP.NET, PHP, and Java applications. With that information, Invicti can identify even more vulnerabilities with 100% confidence.
Frequently asked questions
Qualys is a network security provider specializing in network vulnerability management but only offers limited web application vulnerability scanning functionality and this is spread across multiple products. Functions that are all available in Invicti would require several separate Qualys products, while most advanced Invicti features are not available in Qualys products at all.
You should choose Invicti if you are concerned about web application security and testing your entire web presence for vulnerabilities. Invicti has been developed from scratch as a web application security solution. You should also choose Invicti if you want to scan internal web assets or integrate it into your SLDC. Unlike Qualys, Invicti is also available both on-premises and in the cloud.
Qualys could be a good choice if you are primarily concerned about network security but not web application security. For example, if you have a large company network with thousands of desktop computers and want to continuously manage patching operations. If your focus is on web application security, choose a specialized solution like Invicti instead.
Learn about common cybersecurity assumptions that affect choices.
We use Invicti as part of our security in the SDLC and to test code in DEV and SIT before being promoted to production.