
Invicti Integrations
Invicti integrates with 3rd party applications, making it easier to track and protect against identified vulnerabilities. Invicti scan results can be used by the following Issue Trackers and WAFs, and Invicti can also be used as part of a Continuous Integration environment.

API Discovery
Without the right tools, compiling a comprehensive inventory of an organization’s internal and external API assets is a difficult task. That’s where Invicti comes in. It connects with API management systems and container management tools like Kubernetes to help AppSec leaders and development teams identify, locate, and manage all of their organization’s APIs—including ones that are hidden or undocumented.
To help get the job done, Invicti integrates with:
- MuleSoft Anypoint Exchange
- Apigee API hub
- Amazon API Gateway
- Kubernetes (natively and via Istio Service Mesh)
See also: Introduction to API Sources

Issue Trackers
An Issue Tracker is a powerful and essential tool in the Software Development Life Cycle (SDLC) of almost any software project. It helps development teams streamline collaboration and manage their work without getting lost in an endless stream of emails and PDF reports.
Invicti can send vulnerabilities as issues to the following Issue Trackers:
- Azure DevOps (Microsoft TFS)
- JIRA
- GitHub
- GitLab
- Bugzilla
- Mantis
Web Application Firewalls (WAFs)
Invicti integrates with popular WAFs to automatically create appropriate Web Application Firewall rules to protect web applications against attacks targeting vulnerabilities that the scanner finds. This allows you to temporarily prevent the exploitation of high-severity vulnerabilities until you are able to fix them.
Invicti can export scan data to the following Web Application Firewalls (WAFs):
- Imperva SecureSphere
- F5 BIG-IP Application Security Manager
- FortiWeb WAF
- Citrix WAF
See also: How to integrate with WAFs
Continuous Integration (CI)
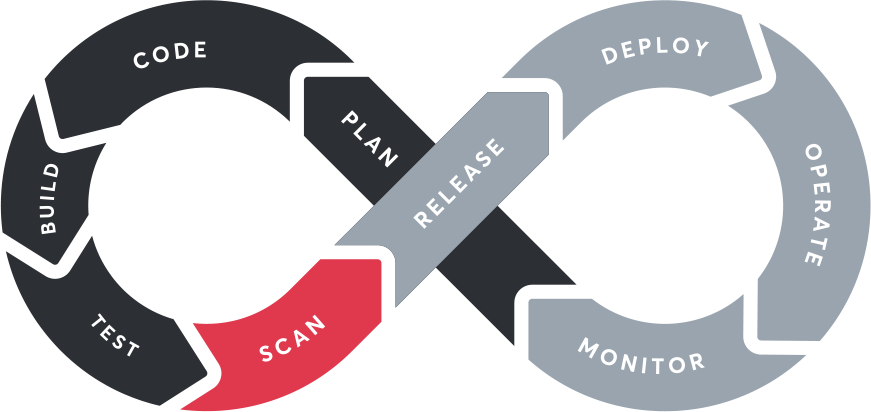
Invicti offers a plugin for Jenkins, a popular open source Continuous Integration (CI) and automation platform. Using this plugin development and operations teams to identify and track web application vulnerabilities early on in the Software Development Life Cycle (SDLC), and crucially, before they make it into production. The Invicti Jenkins plugin integrates seamlessly with the Jenkins build process and triggers automatic Invicti scans as part of the web application build process inside of the Jenkins CI platform.
The Invicti Jenkins plugin enables you to:
- Trigger Invicti scans from within Jenkins upon each build
- Trigger Invicti scans with built-in or custom scan types to only scan for specific vulnerabilities
- Configure Jenkins to fail a build (and optionally abort the scan) as soon as a specific threat-level (high, medium or low severity) is reached
- Automatically generate reports saved within Jenkins
See also: Configuring Invicti Jenkins Plugin
Frequently asked questions
Invicti has out-of-the-box integrations with several issue trackers: Jira, Microsoft TFS (Azure DevOps), GitHub, GitLab, Bugzilla, and Mantis. Acunetix 360 has even more integrations. Integrating Invicti with issue trackers is very simple and straightforward – you just need to establish a connection and then can export vulnerabilities directly to the issue tracker. Our support pages and blog have articles that describe the process.
Acunetix Premium has out-of-the box integration with Jenkins. Acunetix 360 has several other CI/CD integrations. Integrating Invicti with a CI/CD tool is very easy, all you need to do is establish a connection and then you can run Invicti scans directly from CI/CD pipelines.
See a step-by-step guide to integrating Invicti with Jenkins.
Invicti can import data from many different sources: UX tools, proxies, and security analysis tools. An Invicti crawl can be pre-seeded using output from Selenium IDE, Telerik Fiddler, Burp, Paros, and Postman. You can also use the following files to import data into Invicti: HTTP Archives, Swagger, WSDL, WADL, ASP.NET Web Forms, and text files with lists of URLs.
Invicti exposes all its functionality via a REST API. You can use any environment that you like to make REST API calls to Invicti and get the results. This lets you integrate Invicti with any environment that supports REST. In other cases, the Invicti support team can help you figure out the best way to achieve integration.
See an example of how to integrate a custom application with Invicti using the API.
Recommended Reading
Learn more about prominent vulnerabilities, keep up with recent product updates, and catch the latest news from Invicti.
“We use Invicti as part of our Security in the SDLC and to test code in DEV and SIT before being promoted to Production.”
Kurt Zanzi, Xerox CA-MMIS Information Securtiy Office, Xerox