
Scan Anything, Quickly, at Scale
Considering features in dynamic application security tools like Netsparker and Invicti is important. However, speed and accuracy are even more important. Invicti is relentlessly focused on speed. Everything, from the Invicti crawler to every single vulnerability test, is carefully designed to be as quick and efficient as possible. Invicti performs vulnerability scanning up to 10 times faster than other products. Accuracy is the second key advantage of Invicti. Invicti uses the most advanced crawling engine for complex JavaScript and HTML5 applications (single page applications – SPAs) – DeepScan. Just like Netsparker’s Proof-Based Scanning technology, Invicti also provides proof that security issues are real, which also makes its vulnerability testing capabilities fully scalable. In addition to dynamic black-box scanning (DAST), Invicti, unlike Netsparker, allows you to conduct gray-box (IAST) scans thanks to AcuSensor. AcuSensor is a sensor that can be installed on the web server for Java, ASP.NET, and PHP web applications. This brings together the best of dynamic web application security testing together with feedback from sensors within the source code whilst it is in execution.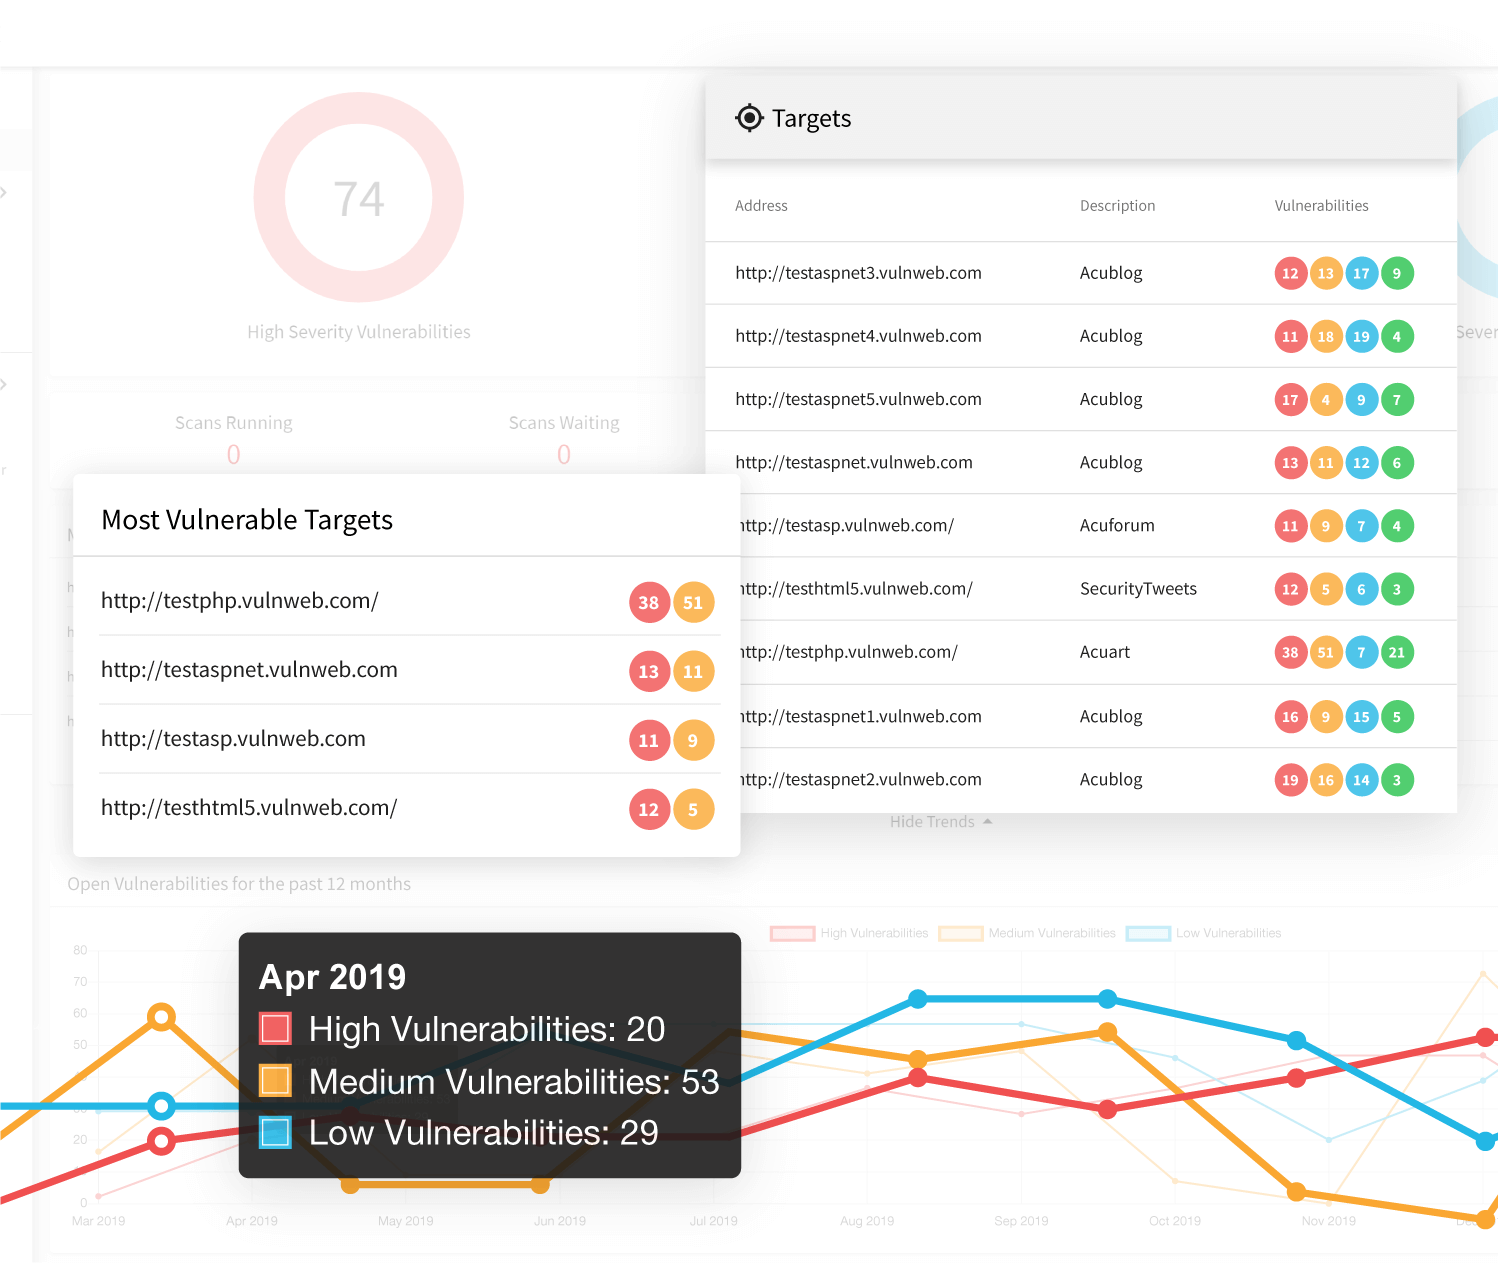
Everything in One Unified Interface
Web security is a game with many stakeholders – from cyber security professionals themselves to development, compliance, and auditing teams and management to name a few. Making sure that all teams have access to the data and reports they need is crucial for a smooth operation of a successful application security program – be they reports, which can be exported to PDFs, HTML files, or even issues opened directly in issue trackers like GitHub, Atlassian Jira, GitLab, Microsoft TFS, Bugzilla, or Mantis. Invicti runs in the browser, meaning that there is nothing complicated to install or configure and users can easily interact in real-time with scan results. With multi-user, multi-role support and built-in vulnerability assessment and vulnerability management tools, Invicti allows everyone to access the same user-friendly web-based interface and reporting. Like the vast majority of security software, Netsparker’s many knobs and levers may be a challenge to use if you’re not a security expert. Invicti, on the other hand, is designed to be dead-simple to use, yet powerful by making the best choices for you. Naturally, there will still be instances where security experts would want to have precise control, and Invicti’s advanced settings allow technical users to do so with ease.Proven in Enterprise, Trusted by Governments
Invicti has been focused on building a best-of-breed web vulnerability scanner for well over a decade, making it amongst the most mature, battle-tested, and widely used web vulnerability scanners. It is used daily by thousands of organizations worldwide ranging from small businesses to Fortune 100 enterprises. It is used both for continuous scanning as well as in SDLC pipelines. Invicti is also the only web application security solution available on four platforms: Windows, Linux, macOS, and cloud.Frequently asked questions
Invicti may be perceived as an alternative to Netsparker but both products are top-class. Both were built by web security experts as web vulnerability scanners and have grown into full vulnerability management solutions. Both introduced leading-edge technologies and both are developed with complete focus on web security and with continued investment into technology.
Invicti always focused on efficiency. The Invicti engine is built in C++ and uses multiple techniques to speed up scans, show ongoing results, and lessen the resource load. On the other hand, Netsparker always focused less on speed and more on scalability and integration for large enterprises.
Invicti can be used as an IAST solution, Netsparker just DAST. Invicti is also integrated with the OpenVAS network scanner and manages all network vulnerabilities together with web vulnerabilities. Invicti is also the only web vulnerability scanner available on Linux and macOS.
For many vulnerabilities, Invicti is able to safely prove that these vulnerabilities are real. The name Proof-based Scanning is used by Netsparker only – Netsparker was the pioneer of this technology. In the Invicti interface, proof of vulnerability is labeled as Proof of Exploit.
Recommended reading
Learn more about prominent vulnerabilities, keep up with recent product updates, and catch the latest news from Acunetix.
“We use Acunetix as part of our Security in the SDLC and to test code in DEV and SIT before being promoted to Production.”
Kurt Zanzi, Xerox CA-MMIS Information Securtiy Office, Xerox