
If you are evaluating web vulnerability scanners for the first time, or struggling to get the best out of Tenable network security products, here is why you should consider Invicti instead.
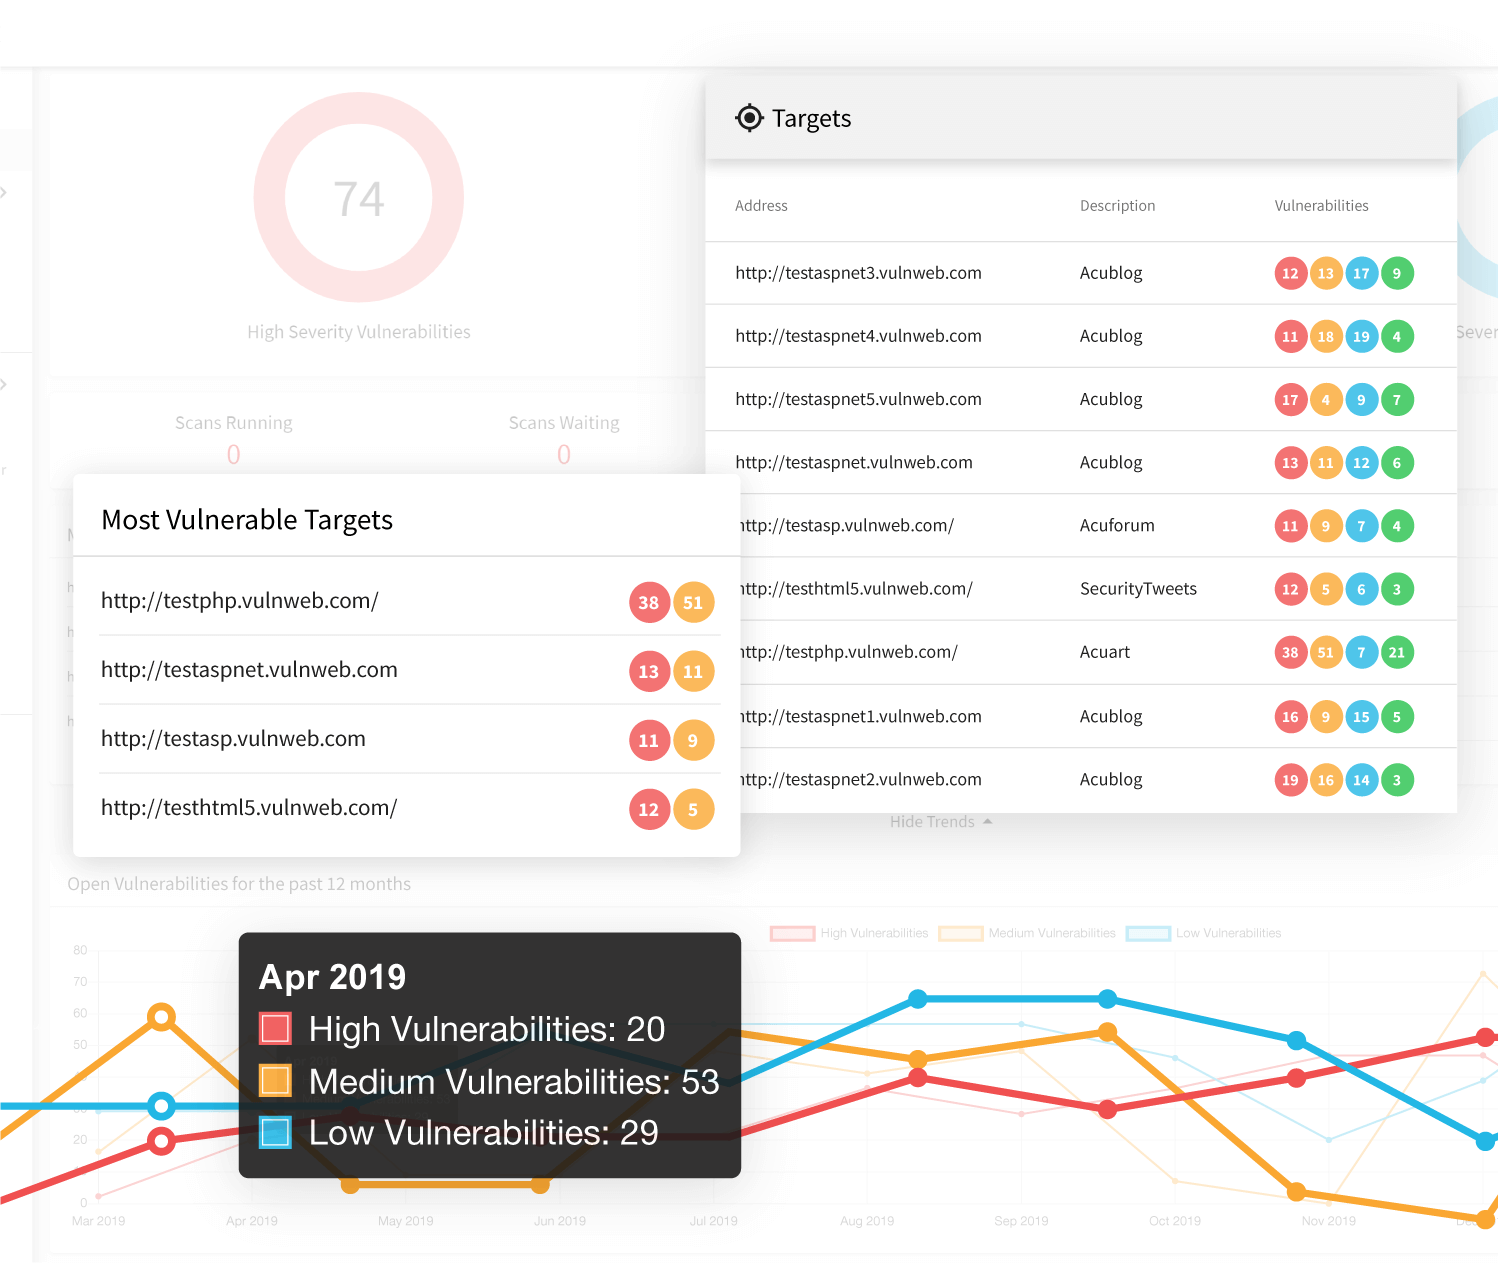
Purpose-built for Web Application Scanning
Tenable Nessus and similar competitors like Rapid7 Nexpose or QualysGuard focus on network vulnerability scanning, which includes mapping out IP addresses, identifying network services running, and finding unpatched network devices. However, reliable web application vulnerability assessment requires a tool built specifically for that purpose. As web technologies evolve and change, you need a tool designed specifically to crawl web applications accurately, identify all resources and inputs, and detect the full spectrum of web vulnerabilities. You need a tool you can depend on to do that now, and in the future.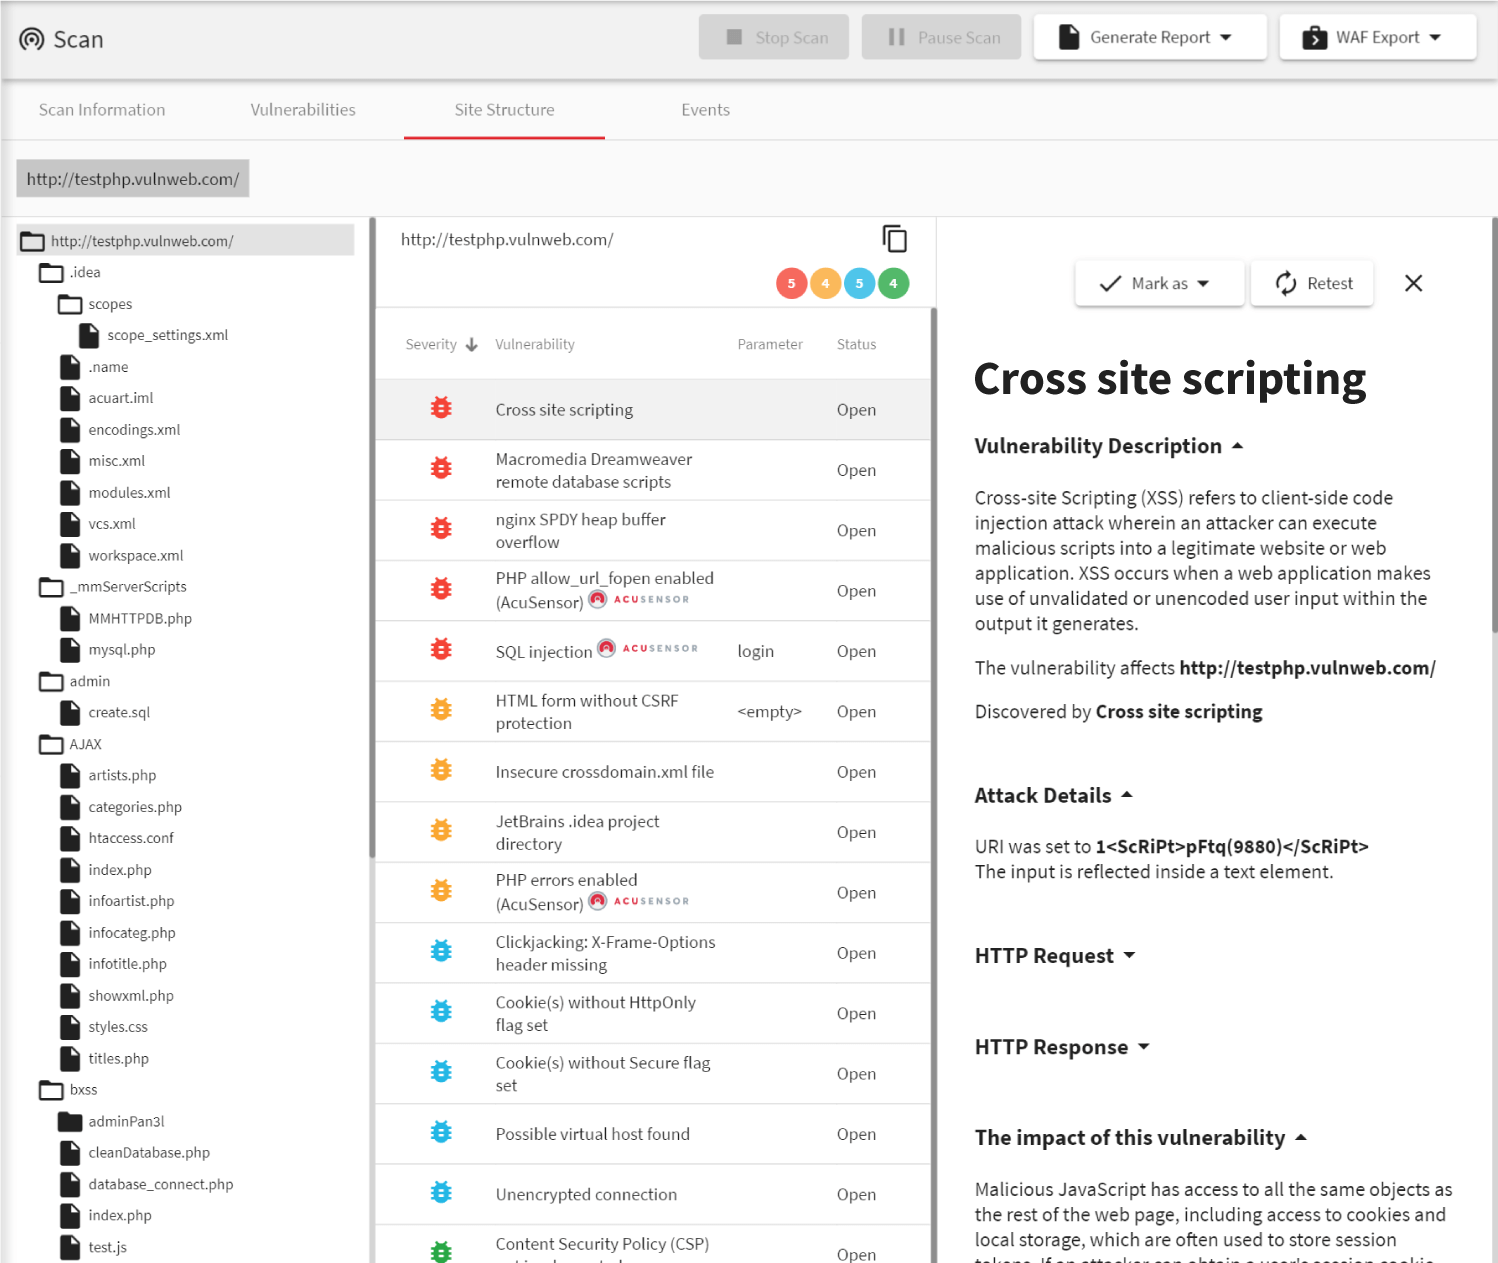
Speed and Accuracy
A network security scanner like Tenable Nessus will have a few web plugins, but it lacks the deep web application analysis engine of a dedicated web application vulnerability scanner. Invicti Vulnerability Scanner, on the other hand, is designed specifically to crawl web applications and identify web vulnerabilities. Its DeepScan engine ensures that whether your business depends on traditional server-side applications or modern single-page applications (SPAs), the scanner will detect all of the inputs and functionality. Invicti detects real web security threats that real-world attackers are searching for, including SQL Injection, Cross-site Scripting (XSS), local and remote file inclusion, weak passwords, and more. These vulnerabilities put your employee, customer, and client sensitive data at risk; to retain their trust, you need a vulnerability assessment tool that helps you find and fix these security threats before attackers do.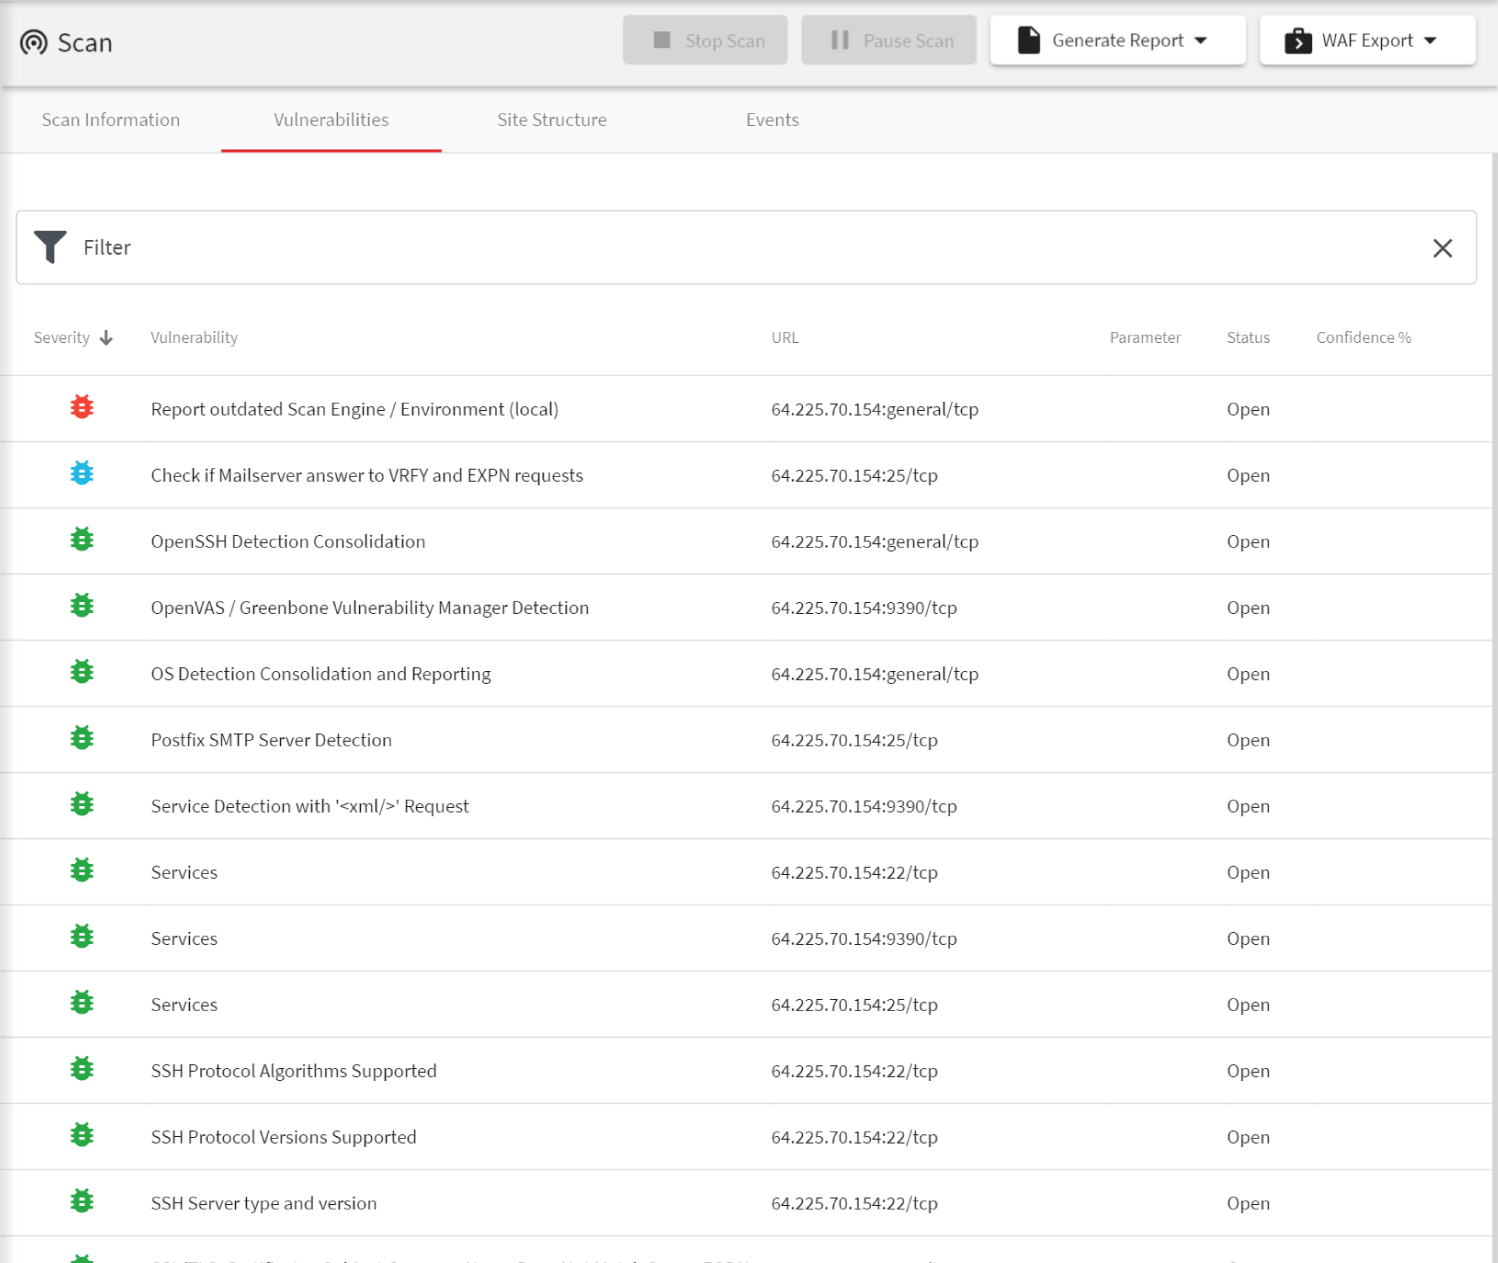
The Flexibility You Need
Regardless of your infrastructure, you will find a version of Invicti that fits your needs. You can run Invicti on your own infrastructure, on Windows, Linux, or macOS. All versions give you our trademark speed and accuracy. For businesses that need to scan large volumes of web applications on-premises, Invicti provides a multi-engine option that allows you to set up several instances of Invicti controlled from a central console. For teams that prefer cloud security solutions, Invicti Online gives you all the key features of our web application vulnerability scanner from a secure cloud portal.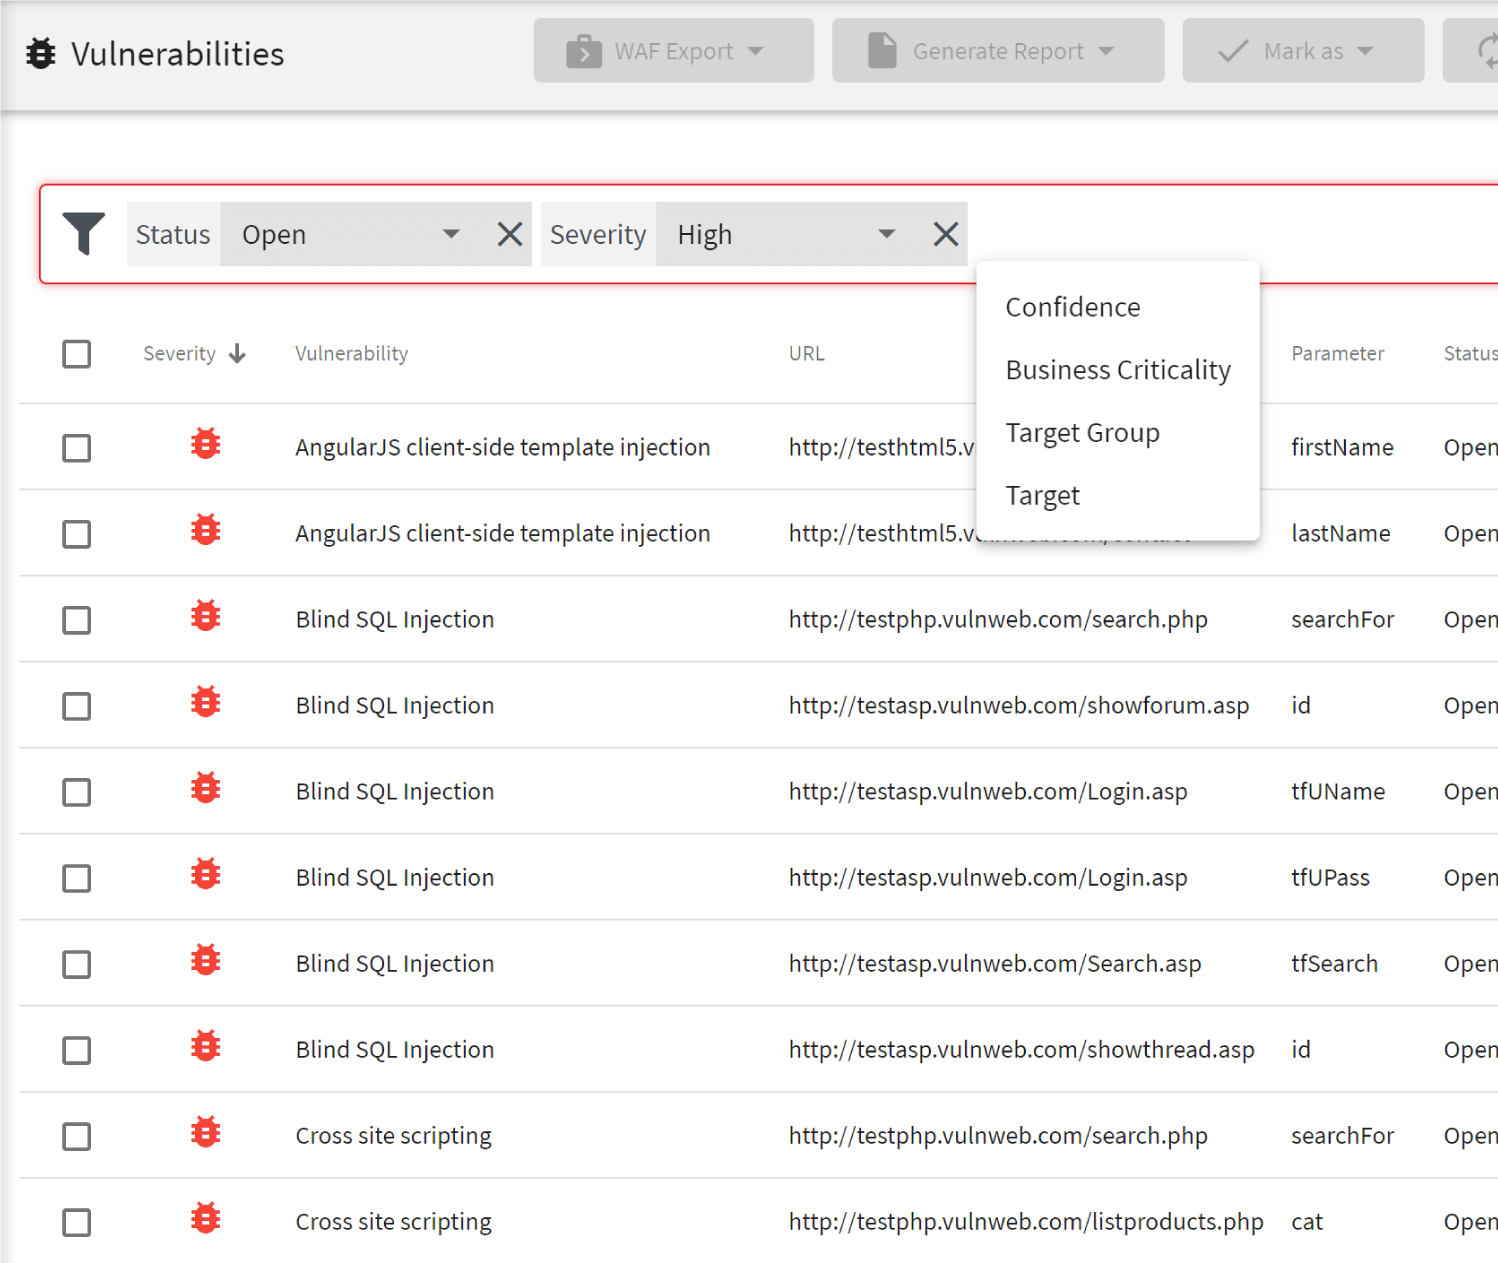
Built-in Vulnerability Management Tools
Your team needs to streamline its web application vulnerability management processes. It matters now and will matter even more as your business expands its web footprint. Invicti is more than just a security scanner: you can configure web application scans, schedule them, review the results, and plan remediation through a secure portal. It gives you the advantage of full-featured vulnerability management software, giving you the ability to define web application vulnerability scans, run them, produce vulnerability reports, and track security posture over time – all in one place.Recommended reading
Learn more about prominent vulnerabilities, keep up with recent product updates, and catch the latest news from Acunetix.
“We use Acunetix as part of our Security in the SDLC and to test code in DEV and SIT before being promoted to Production.”
Kurt Zanzi, Xerox CA-MMIS Information Securtiy Office, Xerox